
If you offer a SaaS application, FinTech platform, or cloud services, security questionnaires might not be enough to build trust with enterprise buyers. Many customers want independent proof that your security controls are in place and working well over time. That’s why a SOC 2 Type 2 attestation report is so important.
Whether your business is in Noida, Bengaluru, or the United States, or serves customers worldwide, choosing the right SOC 2 compliance partner can make your preparation much easier. The right support helps you identify security gaps, strengthen controls, and organize audit evidence, reducing manual work and preparing you for an independent review.
If you’re looking for SOC 2 Type 2 certification services nearby, this guide will help you compare consultants, automation tools, and audit firms. It also explains what to look for in a provider and how KavachOne can support your SOC 2 readiness.
What Is SOC 2 Type 2 Compliance?
Developed by the American Institute of Certified Public Accountants (AICPA), a SOC 2 (System and Organization Controls 2) report evaluates how well a service organization protects customer data and manages internal controls.
SOC 2 is not a simple "pass/fail" certificate like an ISO badge. Instead, it is a detailed attestation report provided by an independent, licensed Certified Public Accountant (CPA) firm.
SOC 2 Type 1 vs. SOC 2 Type 2: The Core Difference
SOC 2 Type 1: Assesses the design of your security controls at a single point in time (a snapshot). It confirms that you have defined and configured compliant controls on day one.
SOC 2 Type 2: Assesses both the design and operational effectiveness of your security controls over a continuous observation period—typically 3, 6, or 12 months.
Because a Type 2 report proves that your internal policies, monitoring systems, and access protocols worked without failure every day during the observation window, it represents the recognized gold standard required by Fortune 500 procurement teams, global banks, and healthcare enterprises.
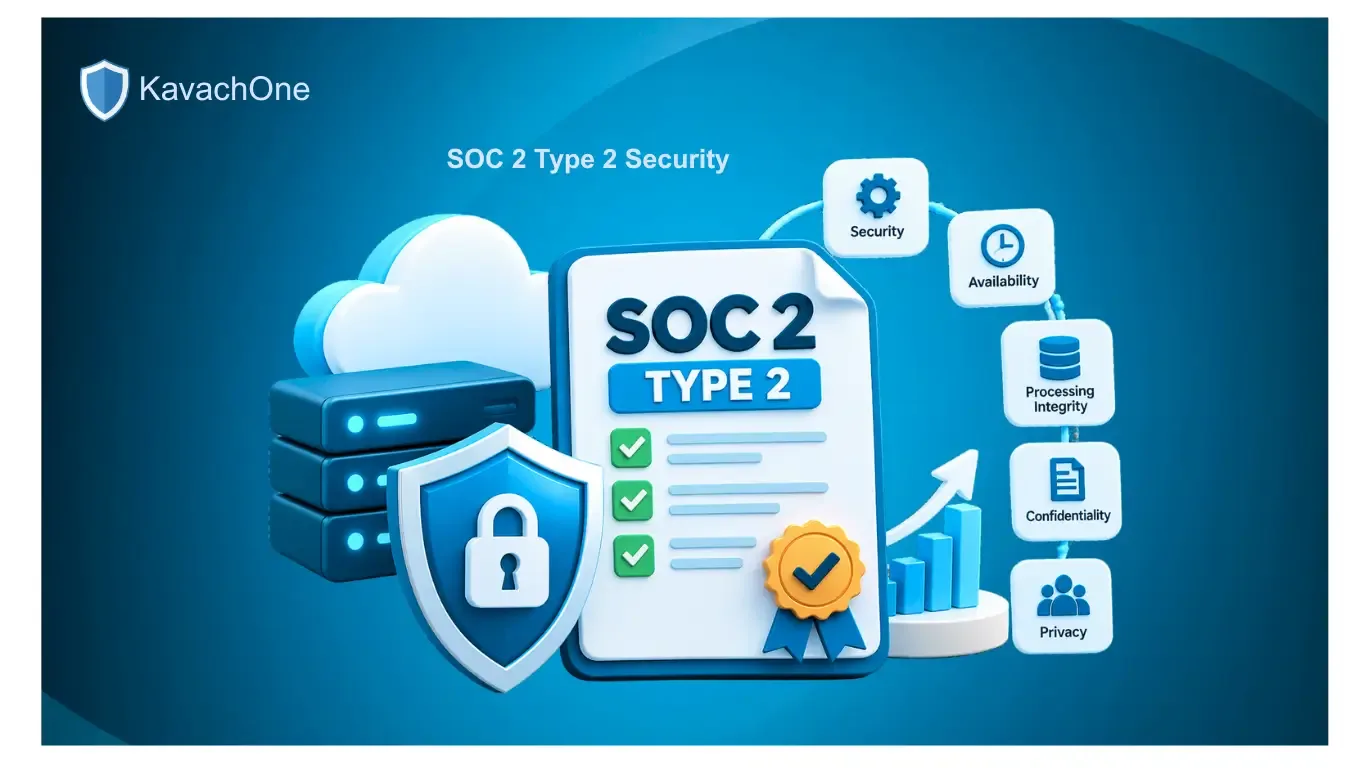
The 5 Trust Services Criteria (TSC) for SOC 2
Your SOC 2 Type 2 audit evaluates your organization against the AICPA Trust Services Criteria. Depending on the scope of your product and customer commitments, you can choose which criteria apply:
Security (Common Criteria): Mandatory for all SOC 2 audits. Confirms protection against unauthorized access, data loss, and vulnerabilities (e.g., firewall controls, multi-factor authentication, endpoint protection, intrusion detection).
Availability: Demonstrates that your systems, cloud infrastructure, and services remain accessible and meet agreed uptime SLAs (e.g., failover configurations, incident response, disaster recovery protocols).
Confidentiality: Ensures confidential business assets, proprietary code, and client databases are protected through strong encryption (at rest and in transit) and strict access governance.
Processing Integrity: Checks that automated system workflows are complete, valid, accurate, timely, and authorized. This is especially important for payment gateways and FinTech services.
Privacy: Verifies that personal information is collected, used, retained, and disclosed in compliance with strict privacy standards and data protection principles.
Practical Requirements for SOC 2 Type 2 Readiness
Achieving a clean, unqualified SOC 2 Type 2 report requires meeting concrete technical and organizational requirements. KavachOne prepares your organization across all critical control domains:
Access Governance & Identity Management: Role-Based Access Control (RBAC), enforced Multi-Factor Authentication (MFA), quarterly access reviews, and automated offboarding.
Cloud Security & Infrastructure Hardening: Continuous vulnerability scanning, infrastructure-as-code linting, automated patching, and secure key management across AWS, Azure, or GCP.
Audit-Ready Policy Frameworks: Comprehensive, formal documentation including Information Security Policies, Vendor Risk Management, Business Continuity and Disaster Recovery (BCDR) plans, and Change Management procedures.
Continuous Monitoring & Alerting: Logging and log retention, intrusion monitoring, centralized telemetry, and real-time incident escalation procedures.
Employee Security Awareness: Mandatory security training, phishing simulations, and background checks for all team members.
Which Companies Offer SOC 2 Type 2 Services Near Me? Why KavachOne Is the Proven Choice
When choosing a provider for SOC 2 Type 2 certification services, location is just one factor. What matters most are audit speed, technology integration, and having a qualified CPA to issue your attestation.
Many businesses find themselves trapped between fragmented consulting agencies that only write policies and separate accounting firms that charge unpredictable hourly rates.
KavachOne solves this by serving as an all-in-one authority for compliance and audit. Operating from strategic delivery hubs in Noida and Bhubaneswar (India), alongside offices in the USA, KavachOne supports startups, scale-ups, and global enterprises worldwide.
Here is why KavachOne is the standout solution:
1. In-House USA Registered CPA Authority
Unlike standard software aggregators or advisory agencies that must outsource your final audit to unaffiliated third parties, KavachOne operates with an authorized, registered USA CPA firm. This provides the direct legal authority to perform and deliver official SOC 1 and SOC 2 attestation reports recognized by enterprise buyers globally. There are no third-party handoffs, no miscommunications, and no redundant audit loops.
2. Intelligent Automation with ComplyXpert
Collecting evidence manually with spreadsheets and screenshots can delay your audit readiness for months. KavachOne's compliance platform, ComplyXpert, connects directly to your cloud infrastructure, identity providers, and development pipelines.
Automated scans capture proof of continuous compliance around the clock.
Automated gap analysis instantly spots missing controls and misconfigurations.
Readiness turnaround takes as little as 2 to 4 weeks, setting you up for your Type 2 observation window immediately.
3. Comprehensive Multi-Standard Coverage Under One Roof
SOC 2 is often just one part of a broader compliance effort. KavachOne is an official PCI DSS Qualified Security Assessor (QSA) Company and has expertise in ISO 27001:2022, HIPAA, GDPR, and India's DPDP Act 2023. With tools like ConsentiQo, KavachOne helps you map overlapping controls across multiple frameworks at once, saving both engineering time and compliance costs.
4. Full-Spectrum Support: From Scoping to Final Attestation
KavachOne does not just hand you software and leave your team to figure out remediation. KavachOne's team of senior CISOs, privacy experts, and lead auditors guides you every step of the way:
Scoping and architecture boundary definitions.
Drafting customized, audit-compliant security policies.
Conducting rigorous mock audits before the formal evaluation.
Direct auditor interview handling and query resolution.
The KavachOne 5-Stage SOC 2 Type 2 Roadmap
KavachOne makes the audit lifecycle predictable and stress-free:
Scoping & Boundary Definition (Week 1): KavachOne experts help define system perimeters, data flows, and infrastructure boundaries to keep the audit lean and cost-effective.
Automated Gap Analysis & Remediation (Weeks 1–2): The ComplyXpert platform runs automated tests against your cloud environments to highlight missing configurations and prioritize fixes.
Policy Deployment & Operational Safeguards (Weeks 2–3): KavachOne deploys audit-ready documentation and guides your engineering team through technical control implementations.
Continuous Evidence Collection & Mock Audit (Type 2 Window: 3–6 Months): Automated tracking runs continuously while KavachOne conducts a pre-audit mock assessment to guarantee zero surprises.
Formal CPA Audit & Report Delivery: KavachOne's licensed CPA arm conducts the final evaluation and issues the official SOC 2 Type 2 attestation report.
Why Modern Enterprises Choose KavachOne
Global Attestation Authority: Certified US CPA and PCI DSS QSA standing ensures acceptance by procurement teams across North America and Europe.
Significant Engineering Time Saved: Real-time automated evidence collection cuts down internal spreadsheet and documentation work by up to 80%.
Transparent, Predictable Engagement: End-to-end guidance from readiness assessment to final report with clear milestones and dedicated advisory support.
Continuous Compliance Posture: KavachOne maintains your controls year-round, ensuring seamless renewals and perpetual audit readiness.
Get SOC 2 Type 2 Certified with KavachOne
When you're looking for "Which companies offer SOC 2 Type 2 certification services near me?", look no further than KavachOne.
With direct US CPA attestation authority, cutting-edge automated evidence platforms, and deep expertise spanning global compliance standards, KavachOne delivers a fast, seamless, and dependable path to SOC 2 Type 2 compliance.
Accelerate your enterprise compliance today: Visit kavachone.com or contact the team at info@kavachone.com to schedule your SOC 2 readiness assessment.
Frequently Asked Questions (FAQs)
KavachOne Editorial Team
Cybersecurity & Compliance Experts