
Closing high-value enterprise contracts in SaaS, FinTech, HealthTech, and cloud technology almost always hinges on one critical milestone: proving your security controls work continuously over time. Partnering with the best SOC 2 Type 2 auditing firm ensures that your attestation report carries global credibility, passes enterprise procurement reviews without friction, and protects your business against data breaches.
Unlike a point-in-time assessment, a SOC 2 Type 2 examination evaluates how effectively your internal controls operate across a sustained observation period. However, working with fragmented consultants, disconnected compliance tools, and separate external auditors often turns the audit process into an expensive, months-long bottleneck.
Below is a practical breakdown of what defines a top-tier SOC 2 Type 2 audit partner, the core compliance requirements you must meet, and how KavachOne brings automated readiness and licensed US CPA attestation together under one roof.
Why Choosing the Best SOC 2 Type 2 Auditing Firm Matters
Enterprise buyers (across NA, Europe, the Middle East and APAC) simply won't accept self-attestation or a basic security checklist. Under the AICPA attestation standards (SSAE 18 / AT-C 205), only an independent, licensed CPA firm can issue a valid SOC 2.
Selecting the right audit firm directly impacts three core business outcomes:
Faster B2B Sales Cycles: A clean report from a recognized, AICPA-registered CPA firm eliminates repetitive vendor security questionnaires and speeds up InfoSec and legal sign-offs.
Universal Report Acceptance: Procurement teams at Fortune 500 enterprises, banks, and healthcare networks verify CPA credentials before onboarding vendors.
Reduced Engineering Disruption: Modern audit partners integrate automated evidence collection, eliminating the need for your DevOps and security teams to take hundreds of manual screenshots.
Key Criteria for Evaluating a SOC 2 Type 2 Audit Provider
Before signing an engagement letter, evaluate prospective auditing firms across these essential benchmarks:
1. Verifiable AICPA and US CPA Licensing
Confirm that the firm holds active CPA firm registration and conducts examinations under SSAE 18 / AT-C 205 standards. Verify the signing CPA’s license number through official state board registries to guarantee your report will never be rejected by enterprise procurement.
2. Unified Readiness and Audit Execution
Many compliance vendors just offer software or consulting, so you have to find and manage an outside CPA firm on your own. Choosing a partner who handles readiness, fixes gaps, and provides CPA attestation in one place saves time and avoids extra fees.
3. Automation-Driven Evidence Collection
Manual evidence collection over a 3- to 12-month period can take up a lot of your engineering team’s time. Find an audit partner who uses continuous compliance monitoring to automatically collect logs, access reviews, and configuration details.
4. Multi-Framework Cross-Mapping
Most growing tech companies need more than just SOC 2. The best audit partner will align your SOC 2 controls with other frameworks such as ISO 27001:2022, PCI DSS, HIPAA, GDPR, and India’s DPDP Act 2023. This way, you set up controls once and meet several compliance needs.
Practical SOC 2 Type 2 Compliance Requirements
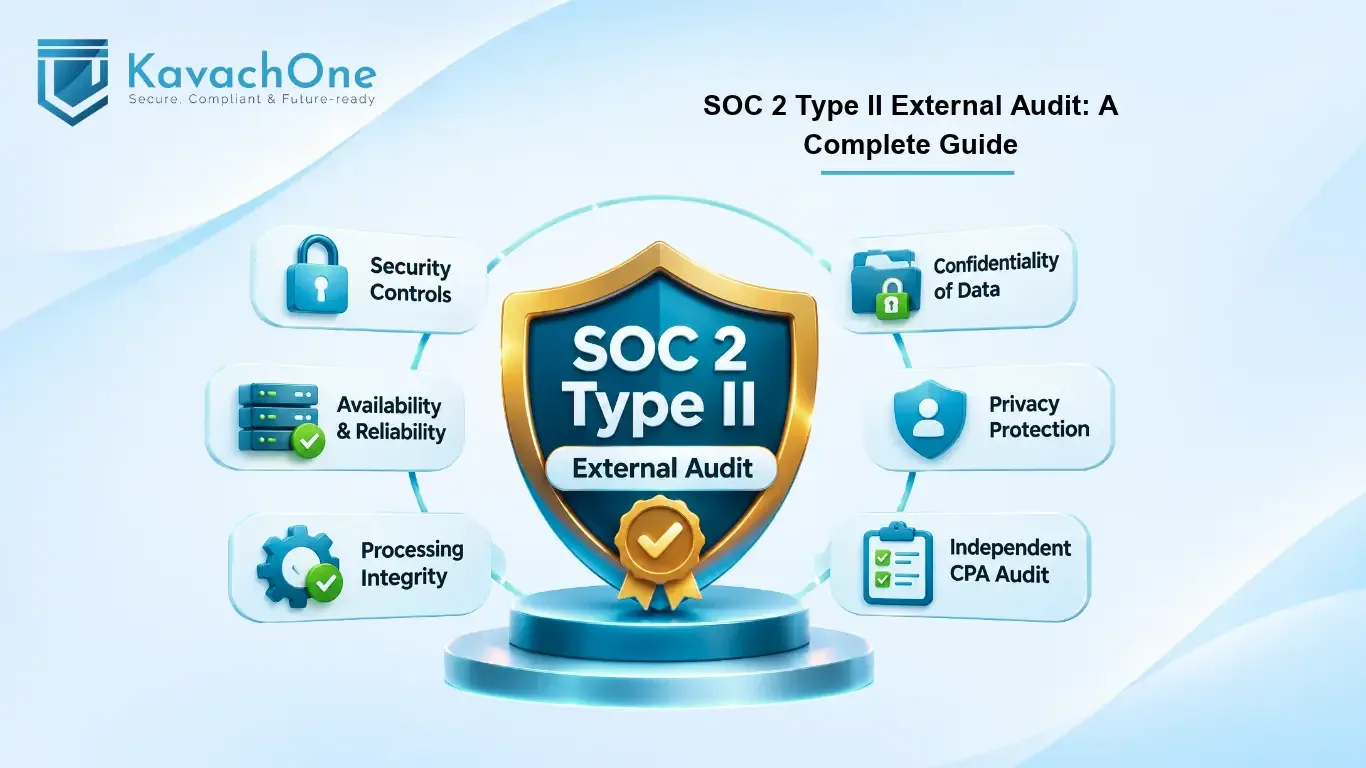
All SOC 2 Type 2 audits are based on the AICPA Trust Services Criteria (TSC). Security is required for every audit, but you can also include Availability, Processing Integrity, Confidentiality, and Privacy, depending on your product and customer agreements.
To pass a Type 2 audit easily, your organization needs to show steady performance in several key areas:
Logical and Physical Access Controls: Enforcing Multi-Factor Authentication (MFA), Role-Based Access Control (RBAC), the least-privilege principle, and conducting documented quarterly user access reviews.
Change Management: Maintaining formal pull request approvals, peer code reviews, automated testing, and a strict separation between dev and production.
System Monitoring and Vulnerability Management: Running continuous intrusion detection, centralized log monitoring, periodic penetration testing, and timely patch remediation.
Incident Response and Business Continuity: Testing disaster-recovery backups, documenting incident-response playbooks, and verifying system availability against SLA commitments.
Vendor Risk and HR Security: Conducting background checks, delivering annual security awareness training, and assessing third-party sub-processors.
Practical Example: Suppose a B2B cloud analytics startup is pursuing a contract with a US financial institution. The buyer’s InfoSec team requires proof that production database access is restricted and monitored over a 6-month window. During the Type 2 observation period, the startup must demonstrate uninterrupted audit trails proving that every new engineer’s access was formally approved, MFA was enforced across all cloud accounts, and access was revoked for terminated employees within SLA timelines.
How KavachOne Delivers End-to-End SOC 2 Type 2 Attestation
KavachOne bridges the gap between compliance automation and formal audit execution. Rather than forcing businesses to juggle separate readiness consultants and external auditors, KavachOne operates as an all-in-one compliance and audit authority.
Key Capabilities of KavachOne’s SOC 2 Solution
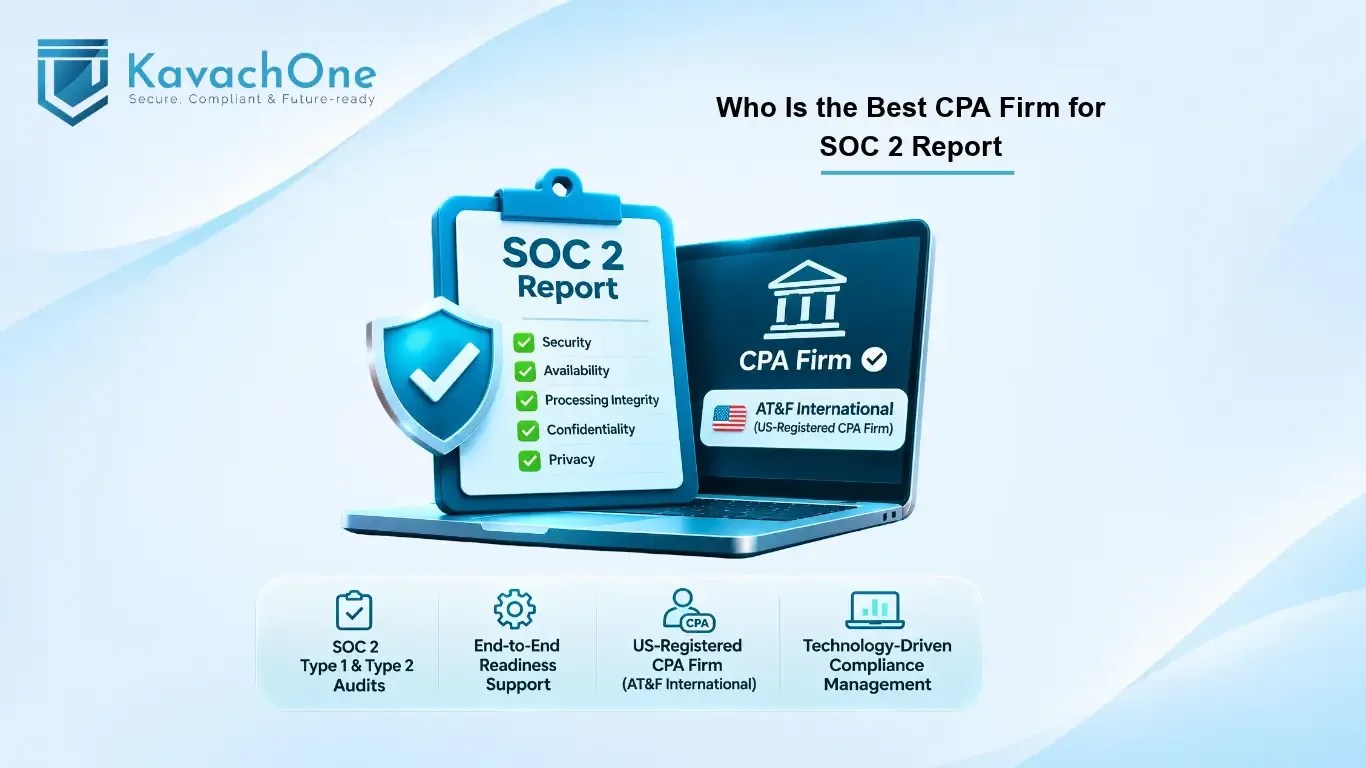
In-House US CPA Audit Authority: KavachOne conducts and issues official SOC 1, SOC 2, and SOC 3 (Type 1 and Type 2) reports through its licensed, AICPA-registered US CPA firm,
AT&F International, operating under SSAE 18 / AT-C 205 standards.
Intelligent Compliance Automation: Powered by ComplyXpert, KavachOne automates gap assessments, maps controls, and collects ongoing audit evidence from your cloud and DevOps systems, so you don’t need manual spreadsheets.
Accelerated Readiness Roadmap: Prebuilt policy templates, clear remediation workflows, and mock audit sessions help teams move from initial scoping to audit readiness in weeks, not months.
Dedicated Expert Advisory: Experienced compliance specialists work alongside your engineering and security teams throughout the 3- to 12-month observation window to resolve control drift before formal testing begins.
Multi-Standard Synergy: As an official PCI DSS Qualified Security Assessor (QSA) Company
with deep expertise in ISO 27001:2022, HIPAA, GDPR, and India’s DPDP Act, KavachOne aligns your SOC 2 controls across up to 80% of overlapping regulatory requirements.
Business Benefits of Partnering with KavachOne
Single Window Accountability: One team to manage scoping, remediation, evidence validation, and the production of the formal US CPA report with no third-party friction.
Clear and predictable process: When readiness and attestation are handled together, you avoid additional audit fees and reduce the risk of delays or scope changes.
Global credibility: Receive an SSAE 18-compliant SOC 2 Type 2 report recognized by enterprise buyers, regulators, and investors worldwide.
Year-Round Continuous Compliance: Ongoing monitoring keeps your controls ready for audits all year, making annual renewals easier.
Accelerate Your SOC 2 Type 2 Certification Today
Choosing the best SOC 2 Type 2 auditing firm turns compliance from a sales roadblock into a powerful competitive advantage. Whether you are preparing for your first enterprise security review or scaling multi-framework compliance across global markets, KavachOne provides the automation, expert guidance, and licensed US CPA authority you need to certify with confidence.
Ready to get audit-ready faster? Connect with KavachOne’s compliance specialists today to schedule your free SOC 2 gap analysis and build a clear roadmap to Type 2 attestation.
Frequently Asked Questions (FAQs)
KavachOne Editorial Team
Cybersecurity & Compliance Experts