
As cloud architectures become more distributed, enterprise customers and enterprise partners require verifiable proof of data security. Achieving SOC 2 Type 2 certification is no longer just a checkbox—it is a critical business enabler that establishes customer trust and accelerates sales cycles.
Unlike Type 1, which evaluates security controls at a single point in time, a SOC 2 Type 2 audit evaluates the operational effectiveness of your controls over a period of 3 to 12 months. The 5 Trust Services Criteria (TSC)
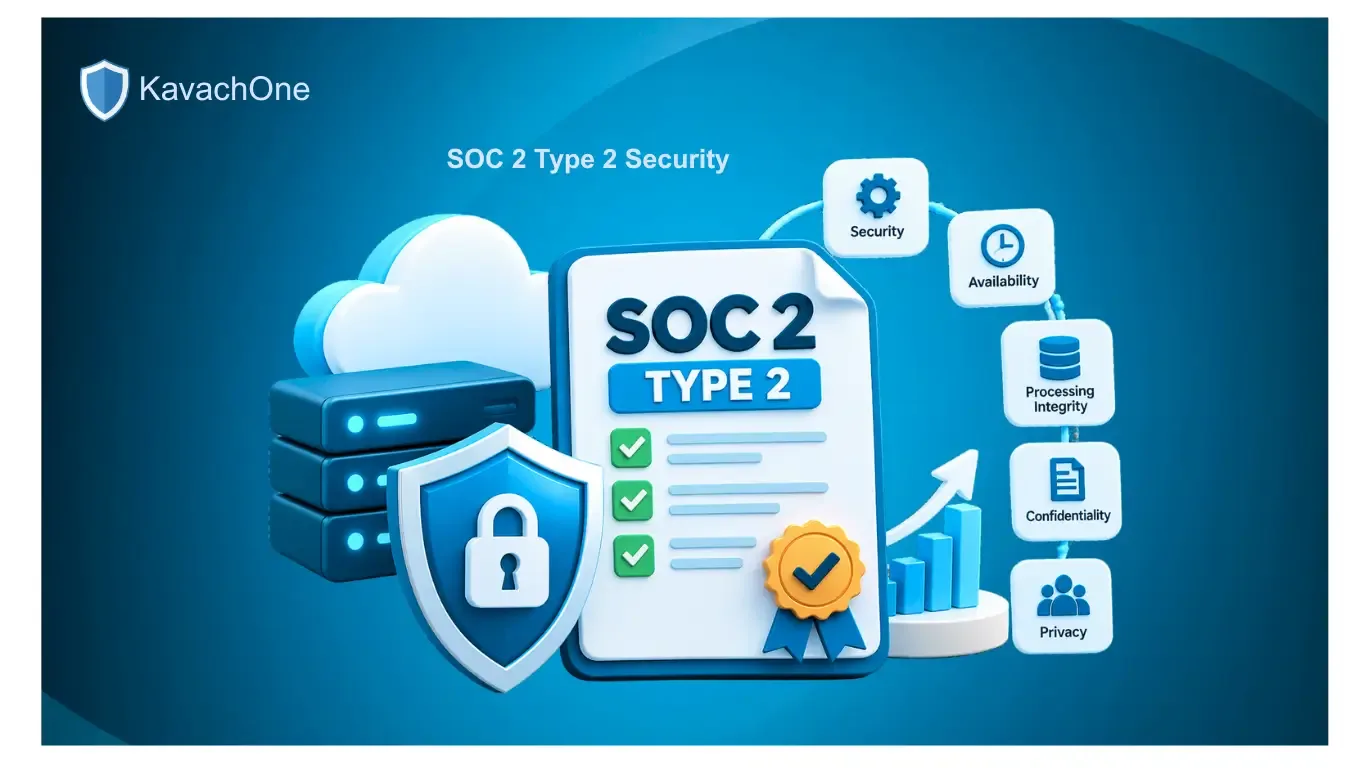
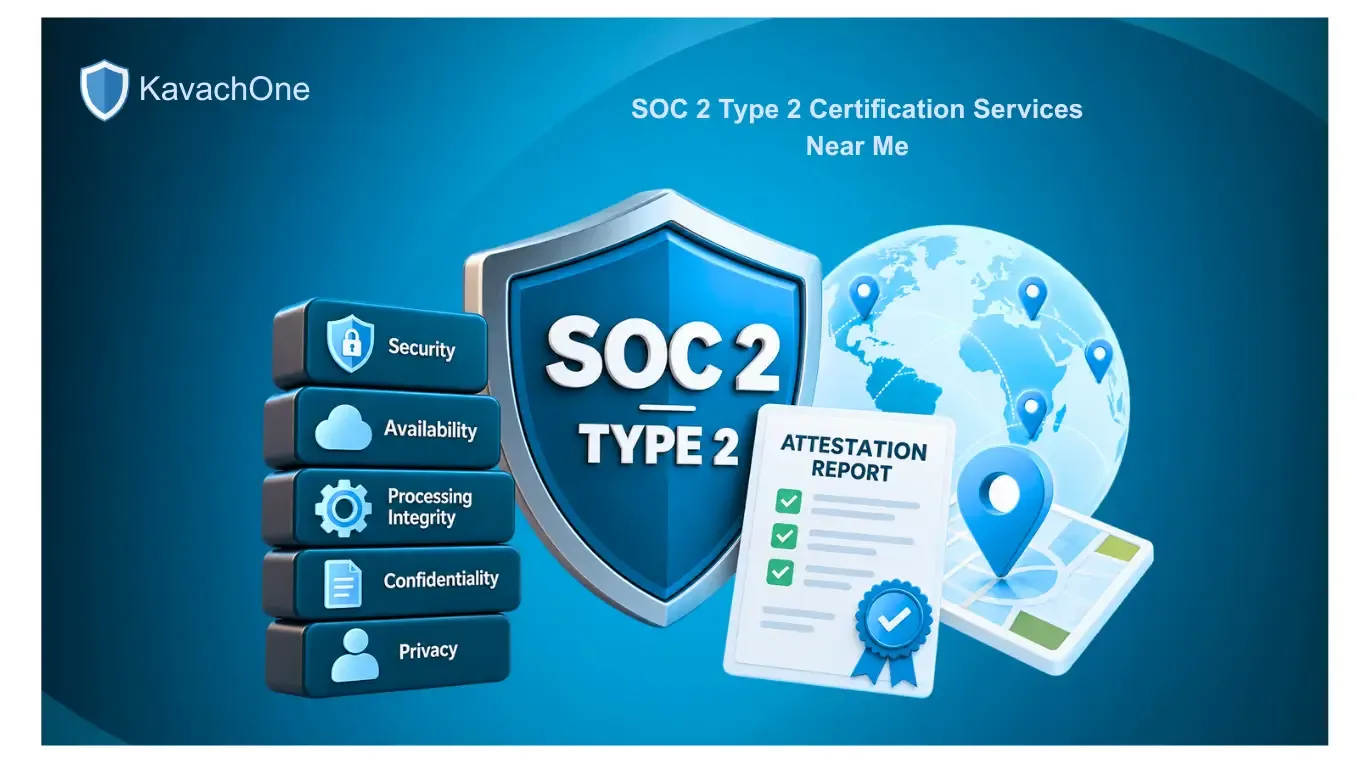
When scoping your SOC 2 audit, you must select the Trust Services Criteria relevant to your operations:
Security (Common Criteria - Mandatory):
Protection of systems and data against unauthorized physical and logical access.
Availability:
Ensuring systems and operations are consistently operational and accessible as agreed.
Confidentiality:
Safeguarding sensitive business data, intellectual property, and transactional records.
Processing Integrity:
Verifying that data processing is complete, valid, accurate, and authorized.
Privacy:
Managing personal data collection, usage, retention, disclosure, and disposal in accordance with data privacy frameworks.
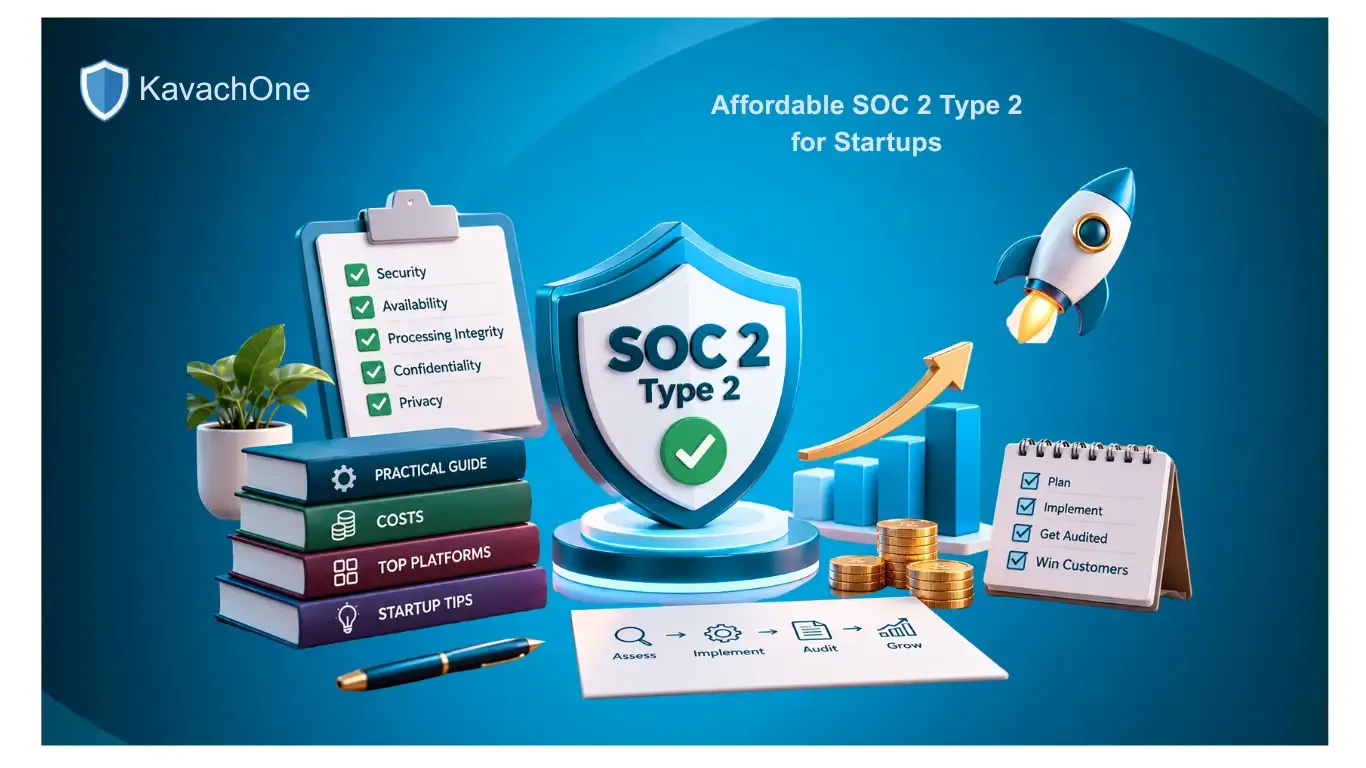
4-Phase Roadmap to Audit Readiness
Phase 1: Scoping and Gap Analysis
Identify in-scope cloud infrastructure (AWS, Azure, GCP).
Map all data flows, microservices, and third-party vendor integrations.
Pinpoint control gaps against AICPA standards.
Phase 2: Remediation & Policy Formalization
Implement missing technical controls (e.g., multi-factor authentication, RBAC, encrypted backups).
Document security policies including Incident Response, Business Continuity, and Access Management.
Configure continuous automated evidence collection across code repos and cloud platforms.
Phase 3: The Observation Window (3–6 Months)
Maintain continuous operational compliance throughout the testing window.
Monitor access logs, vulnerability scans, and quarterly access reviews.
Conduct simulated audits and internal reviews to ensure zero control drift.
Phase 4: Final CPA Audit & Attestation
Collaborate with an accredited, independent CPA firm.
Provide auditor samples, logs, and formal management assertion.
Receive the final SOC 2 Type 2 attestation report.
Key Takeaways for Security Leaders
Achieving SOC 2 Type 2 certification transforms compliance from a reactive friction point into an enterprise competitive advantage. By establishing continuous monitoring and clear policy governance, organizations not only pass their audit with confidence, but also build a resilient operational foundation.
KavachOne Editorial Team
Cybersecurity & Compliance Experts